Tuesday, March 23, 2021

How safe is your data when your staff works from home?

How safe is your data when your staff works from home?

The Coronavirus crisis has changed the world as we know it. With social distancing, lockdowns and work from home becoming the new normal, cyber criminals are exploiting the situation to their gains. This whitepaper discusses how the cyber crime landscape is likely to shape up in the post-pandemic world and how businesses can safeguard themselves against it.

One of the reasons for a sudden spike is cyber crimes is the work-from-home model that is increasingly becoming the norm. When you allow remote access to your data, you are virtually opening your IT infrastructure to criminals--unless you have the right security measures. It is easy for malware and hackers to get into your system and corrupt it unless you have the right measures in place.

With employees operating from home, there are a lot of loopholes that cyber criminals target. Some of them include

Lack of knowledge
Most employees don’t realize how their simple actions or non-actions can contribute to a cyberattack that can bring your whole business down. For example, they may unwittingly end up compromising on your business’s data security by sharing passwords, not using a good antivirus software or using the public WiFi to access their emails, etc.,

It is more difficult to oversee IT operations
With teams working remotely, it is difficult for businesses to manage their IT efficiently. Installation of security patches, anti-malware tools, data backups, etc., are all more difficult now.

Working from home offers businesses a lot of benefits in terms of cost savings, employee satisfaction and flexibility. But, it also raises a lot of questions from the IT security perspective. When opting for the work-from home model, it is important to clearly define the IT policies and put them into practice. You could partner with an MSP who specializes in cybersecurity and remote workspace management to help you formulate a safe, remote working environment.

Monday, March 22, 2021

What Is the Hidden Cost of Security?

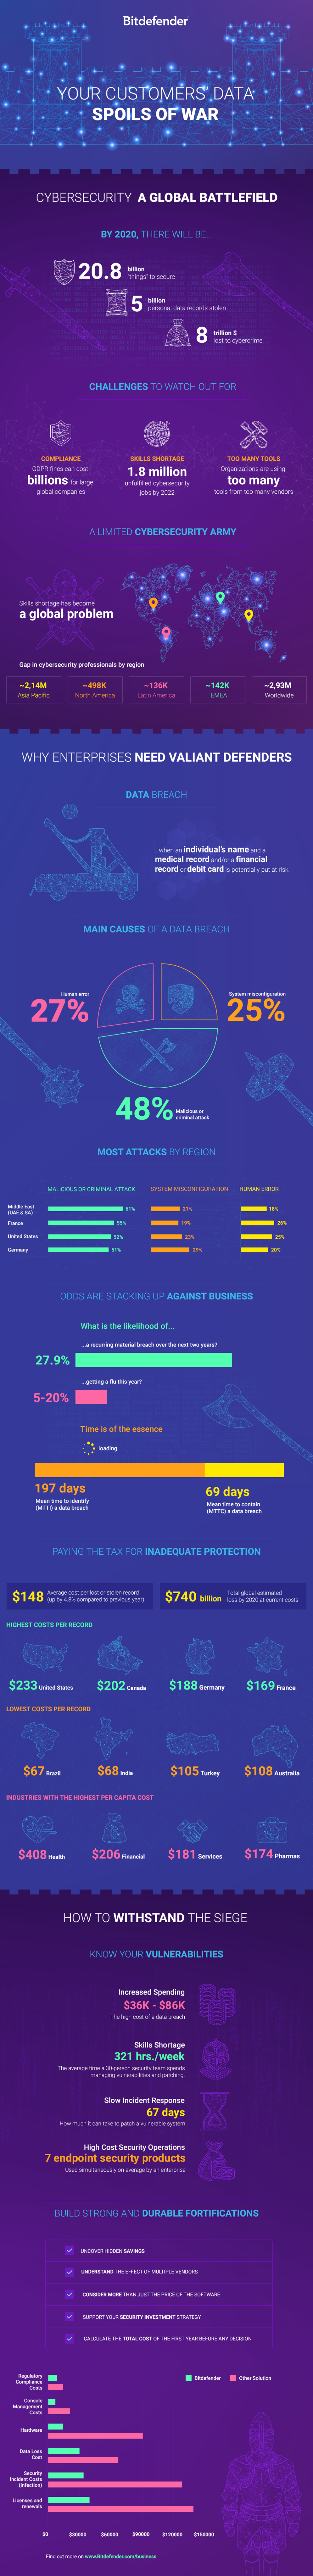
[INFOGRAPHIC] What Is the Hidden Cost of Security?

With less than six months until 2020, experts forecast the industry will be struggling to secure over 20 billion devices from attacks. Cybercrime will never cease to be a money-making machine, with hackers already making trillions of dollars from stealing sensitive data, medical records, financial information and credit history.

And while hackers improve their methods, organizations still don’t understand all the vulnerabilities, gaps and misconfigurations in their IT infrastructure. The global skill shortage leaves millions of jobs unfilled, a major roadblock that businesses need to resolve as soon as possible. Industry research shows that, while 50 percent of global data breaches are caused by malicious or criminal attacks, some 20 percent are the result of human error or system misconfigurations.

Enterprises fail to understand that cyberattacks are no longer a matter of if, but when. So they must not be caught off guard. In the next two years, companies face a 28 percent chance of a recurring material breach. Most firms have inadequate protection. They use software from multiple vendors and usually take over 6 months to identify and contain a breach, leading to the high cost of data breaches. When calculating the total cost of security, senior managers only look at the cost of software, forgetting to include the hidden costs associated with slow incident response, the global skill shortage, and the considerable expense of security operations.

Check out our infographic below to see what to expect from data breaches in the near future.


Tuesday, March 16, 2021

4 things to do to ensure your business continuity planning is a success

4 things to do to ensure your business continuity planning is a success

Working on creating a contingency plan for your business? That’s great! Here are 4 things you need to consider when preparing your new business continuity plan.

Audit of your business continuity plan
Having a business continuity plan alone is not enough. You need to audit it at regular intervals to ensure it is up-to-date and relevant. Often, business continuity plans aren’t used for years, and may be obsolete or irrelevant by the time an actual emergency occurs.

Creating a team for business continuity
Constitute a team for your business continuity project. Decide who will take ownership of implementing the business continuity in the event of an emergency. Break down the business continuity plan into smaller elements and decide who is responsible for each of them. Also, remember to designate a back up for each person in the team.

Mock Drills and Dry Runs
After your business continuity plan is ready you need to check if it really works. A dry run will tell you if it is really effective and also point out to loose ends, if any, that you can fix before the actual emergency.

Don’t forget a debrief
In case you do end up using your business continuity plan, make sure you do a debrief. It will help you determine the effectiveness of your business continuity plan. The brief should focus on identifying the losses you incurred from the disaster, the time taken for implementation of the business continuity plan, the key positives of implementation of your business continuity plan and also offer suggestions, if any for improvement. Irrespective of the size of your business, business continuity planning is indispensable. Bigger companies often have their own staff (IT as well as non-IT) for business continuity planning, but for SMBs to have their own business continuity planning team can be a bit of a strain on their resources. Consider teaming up with a MSP who is experienced in disaster recovery planning, so you don’t cut corners now to regret later.

Tuesday, March 9, 2021

What are the essentials of a business continuity plan?

What are the essentials of a business continuity plan?

An unexpected emergency can wipe out your business! A business continuity plan can help it survive. But, what should a good business continuity plan cover? Read this blog to find out.

A list of your key contacts
One of the most important elements in your business continuity plan is a list of all your important contacts who should be informed of the disaster. This can include all your C-level execs, HR managers, IT Manager, client facing managers, etc.,

A comprehensive list of your IT inventory
Your business continuity plan should contain a list of all the softwares, apps and hardware that you use in the daily operations of your business. This list should identify each of those as critical or non-critical and mention details pertaining to each of them such as
  • The name of the app/software
  • Version/model number (for software/hardware)
  • Vendor name and contact information for each of them
  • Warranty/support availability details
  • Contact information for customer support for these hardware/apps
  • Frequency of usage

Backup information
Data backups are critical to your disaster recovery and so your business continuity plan should include information about data backups. It should mention how often data is backed up, in what formats and where. It should also mention what data backups are available--ideally, you should be backing up ALL data already!

What’s your Plan B?
Make sure your business continuity plan lists a backup operations plan that will come into play in the event of a disaster. Examples include alternative workflows such as options to work remotely or to allow employees to bring their own devices to work (BYOD) until the time regular business premises or systems are ready.

Floor plans and location
Your business continuity plan should also include floor plans of your offices with the exit and entry points clearly marked up, so they can be used in the event of any emergency. It should also mention the location of data centers, phones, key IT systems and related hardware.

Process definition
Make sure your business continuity plan defines the SOPs to be followed in the event of an emergency.

Think business continuity planning is too complicated? Don’t give up! A lot of SMBs, don’t create a business continuity plan thinking it is too much of a hassle. But this can prove fatal to your business later. A qualified MSP can help you understand business continuity planning and even help you create a business continuity plan that’s best suited for you..

Tuesday, March 2, 2021

3 Reasons to prepare a business continuity plan

3 Reasons to prepare a business continuity plan if you haven’t done so already

A business continuity plan is the blueprint you need during an emergency to keep your business running smoothly. If you don’t already have one, here are 3 key reasons why you should focus on creating one ASAP.

It helps retain clients
As a business, if you have problems functioning, it will definitely affect your clients. For example, if your servers are down or your supply-chain mechanism is affected or your delivery process breaks, you won’t be able to fulfill your promise to your clients. Even worse, in some situations you may not even be in a position to communicate about the crisis to your clients adding to their frustration. A business continuity plan addresses these issues beforehand and can help reduce client dissatisfaction.

Salvaging brand image and reputation
There are certain events that end up affecting only your business. For example, ransomware attacks, virus attacks, data leaks, etc., Having a business continuity plan that caters for such events can be a blessing in times of such crisis.

Minimizing revenue loss
A business continuity plan can minimize the revenue losses that occur as a result of a crisis that interrupts your business operations.

In short, a business continuity plan helps minimize the impact of the crisis on your client relations, your brand image and your revenue by equipping you with a plan to handle the situation better.

Tuesday, February 23, 2021

Business continuity planning: A must-have, not a luxury

Business continuity planning: A must-have, not a luxury

Business continuity planning is not an alien concept anymore. In recent times we have witnessed a lot of events that only serve to further intensify the need for business continuity planning. Examples include natural calamities like hurricanes, floods, wildfires, events like terror attacks or even pandemics like the recent Covid-19 outbreak.

While a business continuity plan cannot completely safeguard your business from all these events, it can certainly minimize the damage inflicted on your business. Top business consultants urge their clients to develop a business continuity plan as they consider it a part of the best practices for running a business. A business continuity plan can make the difference between survival and shutdown of a business during a crisis situation.

What is business continuity planning?
Business continuity planning is the process of creating a blueprint that helps your business respond and recover effectively from an unforeseen mishap. As discussed before, the unforeseen event could range from natural disasters to pandemics, or even accidents that affect just your place of business like a fire or even a cybercrime attack directed at your business in particular--basically, any event that can paralyze your business. A business continuity plan serves as a step-by-step guide that you can follow during an emergency to keep your business running smoothly.

True, a business continuity plan is not a sure shot method to survive a crisis, it won’t instantly eliminate the impact of the disaster, but it gives you the best chances of survival. If you are not sure of what a good business continuity plan entails , you can reach out to a reputable MSP to help you with the preparation and implementation of one.

Friday, December 4, 2020

The Enemy at the Gate


The Enemy at the Gate

As an MSP (Managed Service Provider)  who has been supporting small to mid-sized businesses for over 30 years, one thing I can tell you is that the mindset of "we are too small to be the target of a cyber-attack" is far more widespread than one might think.

Some might accuse me of exaggerating, or spreading FUD (Fear, Uncertainty & Doubt) like so much manure on the garden of business.. But in all fairness, I would say that I am understating the gravity of this phenomena.  The data doesn't lie. A recent Accenture/Ponemon study (PDF) shows that 68% of business leaders feel their cybersecurity risks are increasing, and Verizon found that 43% of breach victims were classified as small businesses.

Now, back to my initial postulation that SMB's seem to have a tendency to underestimate their risk.  How I know this to be true is that I find in many cases when doing cybersecurity assessments of prospective new clients, the most often overlooked facet of their cybersecurity maturity score is the firewall.  If there is one element of a businesses defense system that should not be ignored, it's network infrastructure, especially the firewall.

The simple fact is - an outdated firewall not only is likely to be laced with unpatched vulnerabilities, it also is not equipped to handle the threats todays cybercriminals bring to the party. Proper lifecycle management of perimeter security devices is about 5 years.  By that point, the technology has changed to meet the current level of threat to a point where simple subscription based services can no longer keep up.

Case in point - over 70% of all Internet traffic is secured by SSL encryption. The familiar HTTPS preceding the web URL tells you that the connection between you and that web server is secure.  But is it really? Many firewalls can not inspect SSL traffic, and so it passes directly to your browser, with all the potential vulnerabilities intact.  In fact, many of the bad actors who are perpetrating cyberattacks on all levels of business are working in that same "secure" space because they KNOW, most firewalls are either incapable of ferreting them out, or are not properly configured to do so because of the performance hit that results from deep packet inspection of SSL traffic.  It takes serious horsepower to un-encrypt, scan, and re-assemble SSL traffic.

More concerning to me on these visits is when I see big-box store level wireless routers often found on sale for under $100 and touted as a "firewall" being used in a business setting. Or even worse, just using the modem provided by the broadband provider du jour. Let me help you with this - for free - it's not good! No bueno, sehr schlect, call it what you will, but don't call it a business class firewall.  These devices do not have the intrusion prevention mechanisms, country of origin, BotNet, or malicious content filtering capabilities needed in today's cyberthreat landscape.

Yes, I see you out there with the sheepish grin.. While I might call you out for neglecting your businesses security, I don't blame you. Running a business is expensive, and you were probably given advice by someone, or read a review online, or have fallen victim to an IT support provider that really does not understand cybersecurity..  and so, I won't judge.  I would rather educate business owners on the harsh reality of why they need to work with a professional security focused MSP to ensure that the most critical component in their cyberdefense arsenal is right-sized for their current and mid-term needs.

The average payout for a ransomware intrusion on a typical business network is up to $111,605 (bankinfosecurity.com April 2020 study) and as a small business owner myself, the last thing I want to be doing is footing that kind of bill.  While you may recover from the problem, what is often missed in this calculation is the lost customer confidence that can further erode your bottom line over time.  Having the right firewall is the best first step a small business can take to defend against this type of intrusion, and a small price to pay in comparison to the risk.

With the average time to detect an intrusion ranging from 90 - 180 days, sometimes more, having a strong barrier to intrusion is the best first step you can take other than educating your workforce on how to recognize common threats. (Cybersecurity awareness training should be both mandatory and ongoing, and directed from the top down). The amount of downtime that occurs when a malicious intrusion happens can be staggering. To a a small business, this can often result in becoming the straw that breaks the camels back.  

Investing in the right firewall can mean the difference between long term success and failure. If you have not had a cybersecurity assessment performed in a couple years, partner with a reputable MSP or MSSP (Managed Security Service Provider).  They should be able to sit down with you, determine your organizational cybersecurity maturity level and make the right recommendations to help you safeguard your business.  If you are in the Western Massachusetts, Northern Connecticut area, contact us by web, or call us at (413) 786-9675.

Stay tuned for our next look at securing your business with our upcoming blog on endpoint protection.